
An alert notification is not an incident response. When advisory tickets pile up at midnight, your internal engineers shoulder the heavy lifting of cleanup. If you’re researching Arctic Wolf alternatives for midmarket companies, you already know the operational friction: you need a vigilant partner that neutralizes threats directly, not a platform that merely forwards alarms while multi-year contracts escalate.
Midmarket defense demands hands-on execution. You shouldn’t have to choose between alert fatigue and sudden budget spikes when preparing for complex compliance audits. This guide compares the leading alternatives so you can secure definitive threat containment, predictable operational spending, and direct access to strategic security leadership. Below, we examine which providers isolate attacks at the perimeter and truly protect your business in 2026.
Key Takeaways
- Stop alert fatigue by identifying providers that deliver active, decisive remediation instead of pushing triage tickets back to internal teams.
- Evaluate the leading arctic wolf alternatives for midmarket companies to eliminate sudden multi-year contract escalations and secure predictable operational spending.
- Discover how open telemetry integrations outperform closed sensor deployments to safeguard existing infrastructure without platform lock-in.
- Learn why pairing continuous 24/7 surveillance with dedicated virtual CISO leadership bridges technical gaps and streamlines strict compliance audits.
Evaluating Arctic Wolf Alternatives: Why Midmarket Teams Seek Change
Midmarket IT directors don’t have time to triage endless notifications. Traditional vendor relationships break down when a provider flags suspicious activity, generates an urgent ticket, and dumps the containment burden onto internal staff. This handoff model fuels severe alert fatigue while your overstretched engineers scramble to clean up incidents after hours. Compounding the strain, rigid multi-year contracts and unpredictable licensing tiers complicate long-term budgeting. Vetting arctic wolf alternatives for midmarket companies has become a strategic priority for organizations demanding cost predictability and decisive threat suppression.
True operational resilience requires far more than outsourced log parsing. While baseline Managed detection and response solutions identify anomalies, midmarket teams cannot afford to act as the cleanup crew for remote analysts. When evaluating arctic wolf alternatives for midmarket companies, leaders must look beyond dashboards and verify the provider’s willingness to neutralize threats directly.
Critical Capabilities Midmarket Teams Require Beyond Alert Forwarding
Forwarded alerts don’t stop lateral movement. Midmarket environments require hands-on intervention that severs malicious network connections, quarantines infected endpoints, and restores operational stability without draining internal resources. Effective defense must actively secure hybrid Microsoft 365 environments, validating identity perimeters and closing configuration gaps in real time. True remediation depth means partnering with battle-hardened specialists who take decisive ownership of containment, standing as a protective shield rather than an advisory ticketing desk.
Top Arctic Wolf Alternatives for Midmarket Organizations in 2026
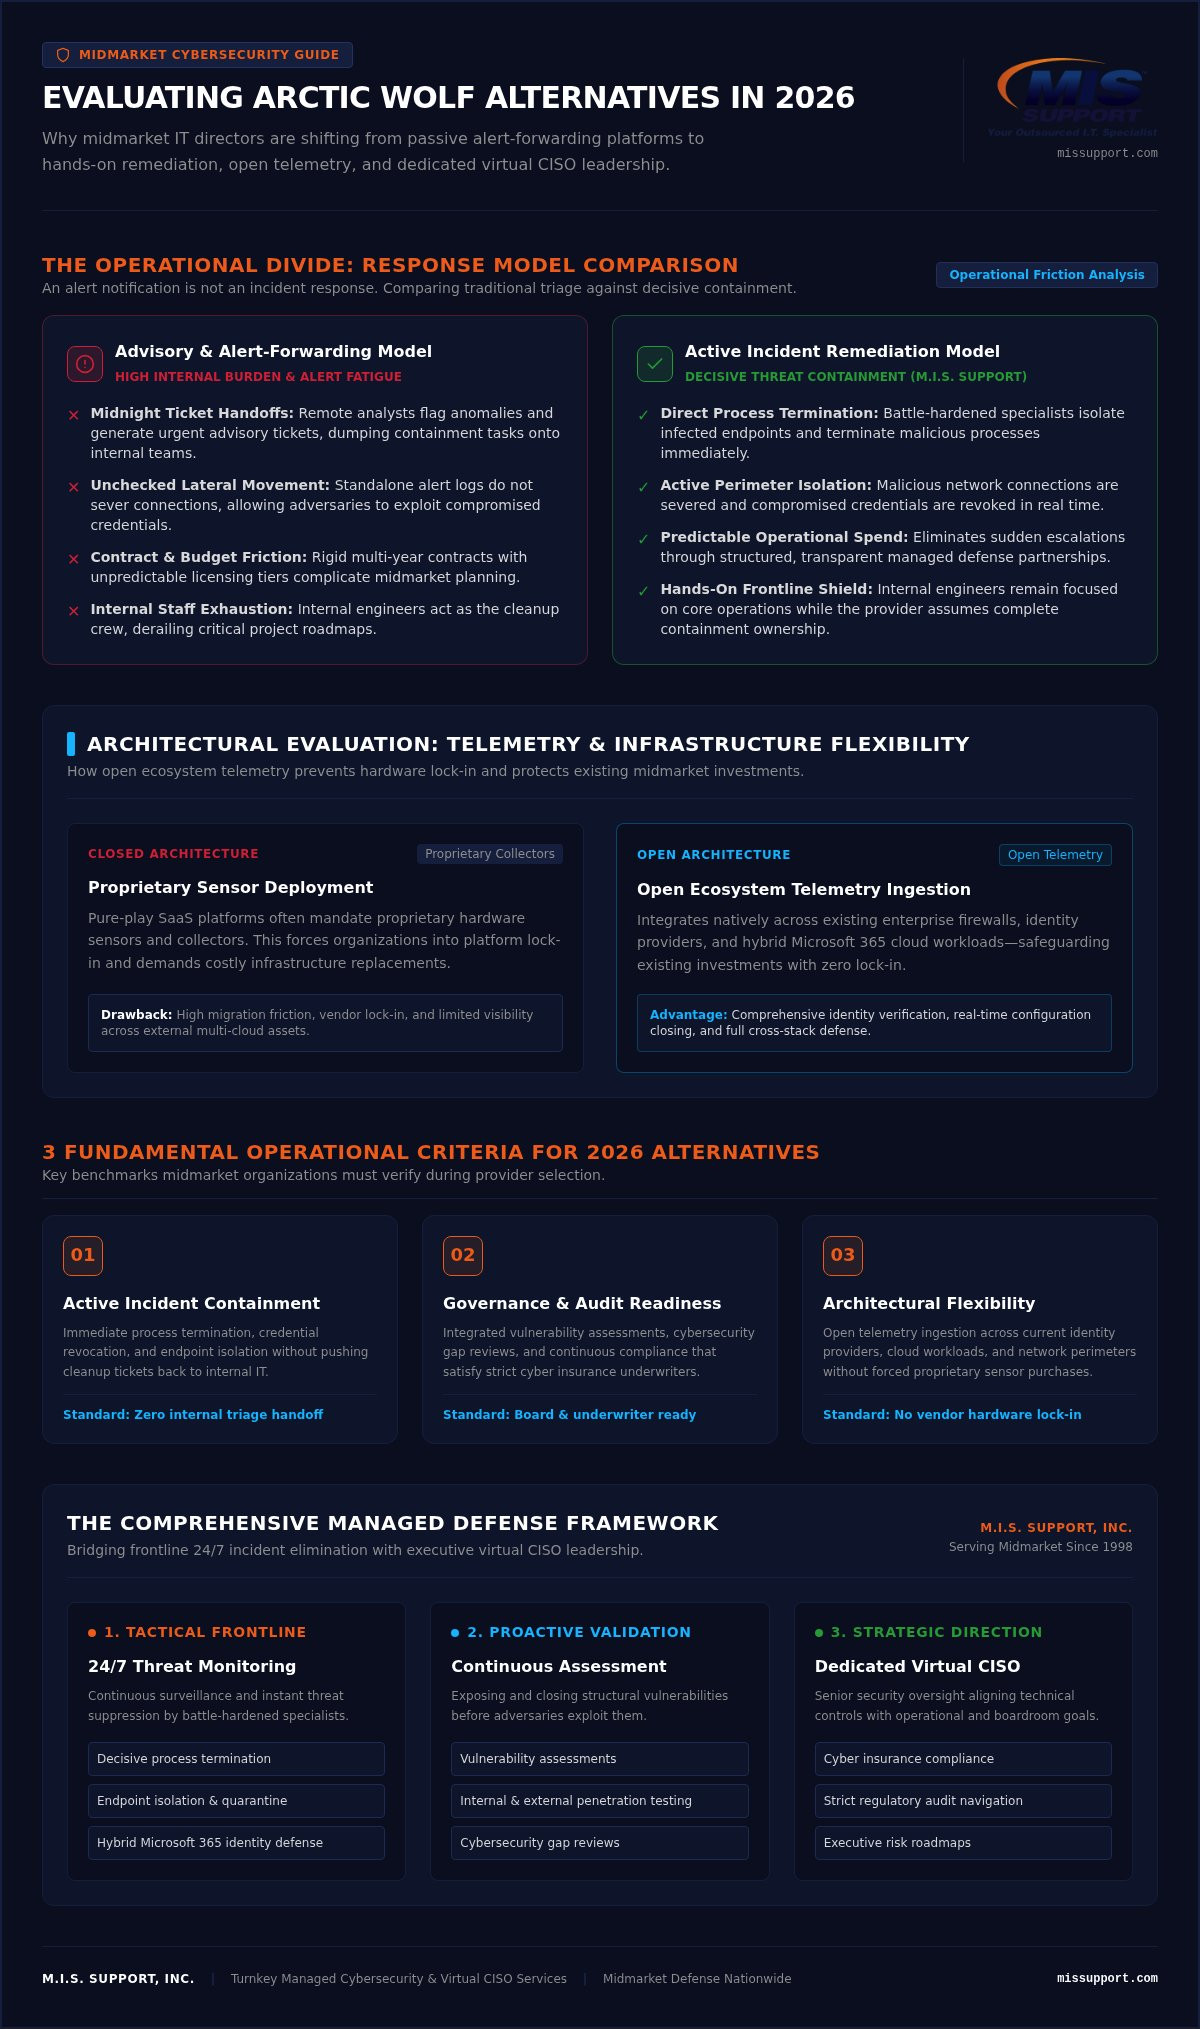
Pure-play SaaS platforms often lock organizations into proprietary hardware sensors. As Gartner defines managed detection and response (MDR), the service focuses on remotely delivered modern security operations center capabilities. Yet evaluating arctic wolf alternatives for midmarket companies reveals a distinct architectural split: rigid proprietary collectors versus open ecosystem monitoring that ingests telemetry across existing firewalls, identity providers, and cloud workloads.
Comparing Dedicated SOC Providers Against Comprehensive Managed Defense
Midmarket infrastructure demands both speed and strategic oversight. Automated script responses stop known commodity threats, but sophisticated adversaries bypass automated heuristics using valid compromised credentials. Standalone MDR tools frequently stop at alert generation, leaving gaps in your defense. Evaluating viable alternatives requires assessing three fundamental operational criteria:
- Active incident containment: Immediate process termination, credential revocation, and endpoint isolation without passing cleanup tickets back to your staff.
- Governance and audit readiness: Integrated vulnerability assessments and compliance management that satisfy cyber insurance underwriters.
- Architectural flexibility: Open telemetry ingestion that defends existing tools without demanding expensive infrastructure replacements.
Choosing turnkey managed cybersecurity services bridges the gap between active threat hunting and long-term risk mitigation. Rather than settling for alert handoffs or unpredictable contract expansions, organizations can partner with a vigilant ally. Discover how M.I.S. Support strengthens organizational defense with decisive 24/7 monitoring and hands-on remediation.
Deploying Direct Threat Remediation with Dedicated Cybersecurity Leadership
Halting a breach requires swift tactical intervention, but building true resilience demands continuous executive direction. Midmarket IT teams frequently run lean, where a single active intrusion derails critical project roadmaps. When evaluating arctic wolf alternatives for midmarket companies, the primary differentiator isn’t just who spots the anomaly; it is who neutralizes the risk and actively guides your governance. Forwarded alerts do not satisfy boardrooms or insurance underwriters.
How M.I.S. Support Delivers Turnkey Threat Elimination and Strategic Governance
Serving midmarket organizations nationwide since 1998, M.I.S. Support operates as a battle-hardened guardian. Our teams provide true 24/7 threat monitoring backed by decisive incident remediation, actively terminating unauthorized processes and isolating compromised endpoints without burdening your internal staff. This hands-on frontline defense works alongside strategic oversight. Through dedicated virtual CISO services, we navigate complex regulatory audits, align security controls with business goals, and maintain rigorous cyber insurance compliance.
Fortification also requires proactive validation. Continuous endpoint defense gains maximum value when paired with rigorous vulnerability assessments, internal and external penetration testing, and structured cybersecurity gap reviews. This layered methodology exposes and closes structural weaknesses before adversaries exploit them. For organizations reviewing arctic wolf alternatives for midmarket companies, integrating active tactical remediation with seasoned executive leadership turns reactive defense into enduring operational strength.
Secure Your Perimeter with Decisive Frontline Remediation
Choosing among arctic wolf alternatives for midmarket companies comes down to one requirement: eliminating internal operational drag through decisive action. Your team can’t afford advisory tickets that leave remediation in your hands, nor should your budget suffer from rigid platform lock-in. Resilient defense demands active containment, continuous 24/7 surveillance, and executive guidance that keeps compliance audits on track.
Safeguarding organizations nationwide since 1998, M.I.S. Support replaces reactive alert noise with dedicated investigation, hands-on threat eradication, and integrated vCISO leadership. Backed by proactive penetration testing, our specialists ensure your network remains fortified against evolving attacks. Take command of your operational security and protect your growth. Fortify your midmarket defense with proactive managed cybersecurity from M.I.S. Support.
Frequently Asked Questions
What is the primary drawback of advisory-only MDR providers for midmarket companies?
Advisory models push the burden of containment back onto internal staff. Instead of resolving intrusions, they log an event and assign your engineers cleanup tickets during critical outages. This practice drains lean IT teams and increases operational downtime, prompting teams to seek arctic wolf alternatives for midmarket companies that deliver decisive, hands-on eradication rather than notifications.
How do Arctic Wolf alternatives handle active threat containment and remediation?
Modern alternatives take direct action across the attack surface. Rather than offering basic guidance, proactive providers terminate rogue processes, sever malicious remote connections, quarantine compromised devices, and revoke hijacked credentials. This turnkey intervention neutralizes active threats immediately, eliminating operational drag and ensuring internal resources stay focused on core strategic projects.
Can an alternative managed security provider integrate with existing Microsoft 365 environments?
Yes, robust providers ingest telemetry directly across Microsoft 365 environments. They continuously validate access controls, identify misconfigurations, and counter identity-based threats without demanding proprietary sensor hardware. When researching arctic wolf alternatives for midmarket companies, look for open telemetry integrations that secure existing cloud collaboration tools alongside firewalls and workloads.
Why do midmarket organizations combine 24/7 threat monitoring with virtual CISO leadership?
Technical surveillance stops immediate digital attacks, but executive leadership establishes enduring security posture. A virtual CISO translates real-time incident data into strategic risk management, aligns safeguards with cyber insurance requirements, and steers mandatory compliance audits. This unified approach bridges daily tactical monitoring with high-level corporate governance for complete operational resilience.