
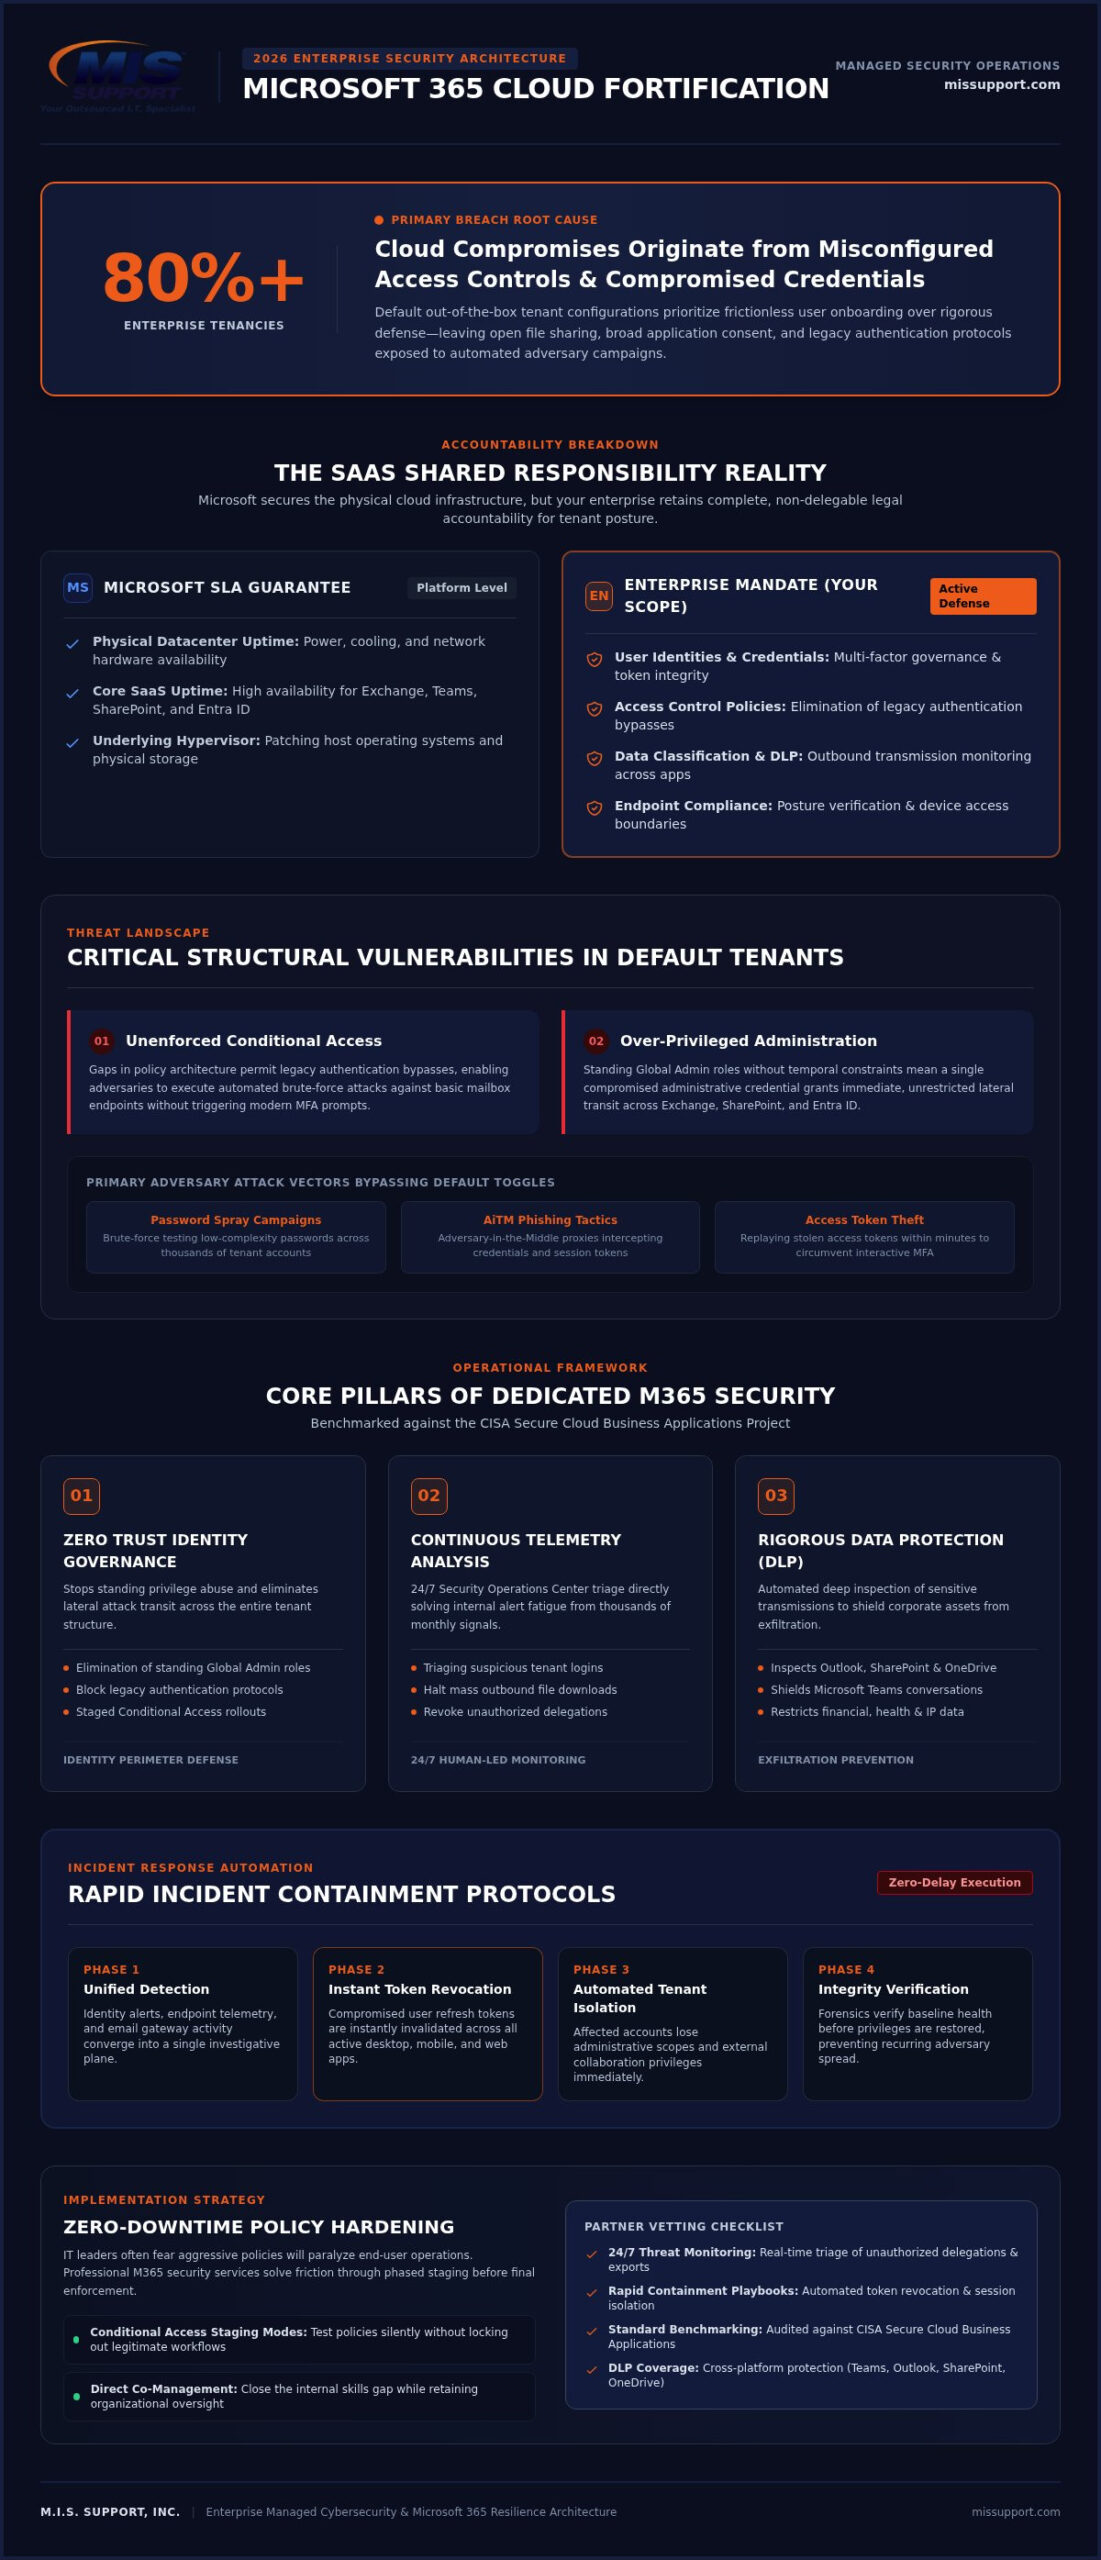
Over 80% of enterprise cloud compromises originate from misconfigured access controls and compromised credentials. Default tenant settings prioritize frictionless user onboarding over rigorous defense, leaving critical entry points exposed to credential theft and ransomware propagation. If your IT team is drowning in alert fatigue, administrative complexity, and 24/7 identity defense demands, you already understand the stakes. Default toggles can’t stop persistent adversaries; safeguarding your organization requires dedicated Microsoft 365 security services engineered for continuous protection.
Discover how dedicated Microsoft 365 security services eliminate configuration vulnerabilities, protect critical identities, and build durable operational resilience. This 2026 enterprise guide breaks down the strategic frameworks needed to establish an impenetrable identity perimeter, achieve verified regulatory compliance, and relieve internal IT personnel through decisive, round-the-clock threat management.
Key Takeaways
- Understand why out-of-the-box cloud settings prioritize administrative convenience over security, creating configuration gaps that expose enterprise tenants to credential theft.
- Discover how dedicated microsoft 365 security services turn passive software licenses into an active, fortified defense backed by round-the-clock engineering oversight.
- Explore the core pillars of tenant defense, spanning continuous telemetry analysis, zero trust identity governance, and aggressive data protection baselines.
- Evaluate prospective national security partners using a clear vetting framework designed to harden policies seamlessly without causing operational downtime.
The Reality of Microsoft 365 Risk: Beyond Default Configurations
Default cloud environments favor user frictionless access over hardened security perimeters. When enterprises spin up tenant infrastructure, standard toggles leave file sharing wide open, enable legacy authentication protocols, and grant broad application consent. Microsoft delivers the underlying platform, but securing the tenant itself falls squarely on your shoulders. True cloud defense demands dedicated microsoft 365 security services that provide continuous managed engineering, real-time threat detection, and active incident remediation.
Adversaries know default defenses rarely stop modern identity intrusions. Password spray campaigns, Adversary-in-the-Middle (AiTM) phishing, and token theft easily bypass standard protections. Relying solely on out-of-the-box licenses creates shelfware; without specialized human oversight, advanced security capabilities sit dormant. Many organizations partner with managed security service providers to close this critical skills gap and implement constant operational oversight.
Critical Misconfigurations That Expose Modern Enterprise Tenancies
Under the cloud shared responsibility model, Microsoft guarantees physical datacenter uptime and core SaaS service availability, while your enterprise retains complete, non-delegable legal accountability for user identities, access policies, data classification, and endpoint compliance. Passive configurations break down under focused adversary testing. Two structural weaknesses routinely create immediate exposure:
- Unenforced Conditional Access: Gaps in policy architecture allow legacy authentication bypasses, letting attackers execute brute-force attacks against basic mailbox endpoints without triggering modern multi-factor prompts.
- Over-Privileged Administration: Standing Global Admin privileges lack temporal boundaries; once an administrative credential leaks, attackers gain unrestricted lateral transit across Exchange, SharePoint, and Entra ID environments.
Closing these gaps demands continuous policy refinement. Professional microsoft 365 security services eliminate standing attack paths, enforce rigorous access controls, and build measurable digital resilience across your entire operating environment. Organizations seeking tailored telecommunications and network infrastructure to support their digital operations can visit SolaaS Limited for expert connectivity insights and solutions.
Core Pillars of Managed Microsoft 365 Security Services
Modern defense demands three operational baselines: identity governance, continuous telemetry analysis, and rigorous data protection. Native portals generate thousands of raw alerts monthly. Without specialized engineering, alert fatigue blinds internal staff to active intrusions. Round-the-clock security operations centers triage suspicious tenant authentications, halt mass file exports, and remediate unauthorized administrative delegations. To establish verified resilience, modern teams benchmark these baselines against the CISA Secure Cloud Business Applications project rather than trusting factory presets.
Data governance requires active boundaries. Automated data loss prevention (DLP) engines inspect sensitive outbound transmissions across Outlook, SharePoint, OneDrive, and Microsoft Teams. By restricting unencrypted financial records, healthcare data, and proprietary intellectual property in real time, professional microsoft 365 security services shield corporate tenancies from deliberate exfiltration and accidental leaks.
Integrating Threat Detection With Rapid Incident Containment Protocols
Containment must be immediate. Modern adversaries weaponize stolen access tokens within minutes. Effective defense converges identity alerts, endpoint telemetry, and email gateway activity into a unified investigative plane. When suspicious lateral movement signals appear, automated containment playbooks execute without delay:
- Instant Session Revocation: Compromised user refresh tokens are instantly invalidated across all active desktop, mobile, and web applications.
- Automated Tenant Isolation: Affected accounts lose administrative scopes and external collaboration access while forensics verify baseline integrity.
Unifying these capabilities within broader managed cybersecurity services establishes a reliable defense framework that stops adversary spread without stalling daily productivity.
Selecting a Strategic National Partner for Cloud Fortification
Selecting the right national defense partner separates proactive fortification from costly disruption. IT executives often fear that aggressive security policies will paralyze end-user operations. A seasoned partner resolves this friction through structured, phased rollouts, deploying Conditional Access policies in staging modes before final enforcement to guarantee zero downtime. When evaluating providers of microsoft 365 security services, demand proven capabilities across 24/7 threat monitoring, rapid incident response, and direct co-management. Integrating your cloud posture with dedicated secure managed IT services bridges the gap between daily operations and uncompromising defense.
Continuous Assessment, Compliance Auditing, and Executive Risk Governance
Cloud security isn’t a static project; it’s an ongoing operational campaign. Tenant configurations naturally drift over time as applications connect, employee roles shift, and cloud platforms evolve. Maintaining verified resilience requires recurring configuration audits aligned with established CIS Benchmarks and federal regulatory mandates.
Routine administration catches misconfigurations, but mature governance requires independent validation. Pairing day-to-day oversight with rigorous third-party penetration testing rigorously evaluates identity perimeters and exposes attack paths before hostile actors strike. Specialized microsoft 365 security services unite continuous administrative vigilance with executive-level reporting, transforming complex cloud risk into measurable business resilience.
Take Decisive Command of Your Cloud Defense
Default cloud settings leave critical gaps that automated licenses alone can’t close. Durable resilience demands proactive engineering, continuous telemetry analysis, and strict identity governance. When you replace passive baselines with battle-tested oversight, you eliminate administrative alert fatigue and stop adversaries before lateral movement begins.
Partnering with seasoned specialists transforms cloud complexity into verifiable operational strength. Backed by nearly three decades of national cybersecurity leadership, M.I.S. Support, Inc. delivers full-spectrum protection by integrating 24/7 threat monitoring, vulnerability management, and virtual CISO guidance. Don’t leave your tenant perimeters to chance. Fortify Your Microsoft 365 Environment with M.I.S. Support, Inc. through dedicated microsoft 365 security services, and give your enterprise the lasting protection it deserves.
Frequently Asked Questions
What is included in professional Microsoft 365 security services?
Professional microsoft 365 security services deliver continuous tenant hardening, 24/7 threat monitoring, identity governance, and automated data loss prevention. Instead of basic IT upkeep, dedicated engineers actively triage alerts across Defender and Entra ID, continuously refine Conditional Access policies, enforce least-privilege administrative access, and conduct rapid incident containment. This turns raw licensing into an active, round-the-clock defensive architecture.
Are built-in Microsoft 365 security features enough to protect my business?
Built-in features offer powerful tools, but they aren’t enough on their own without dedicated operational engineering. Native platform settings prioritize end-user convenience over aggressive defense. Without skilled specialists actively investigating anomalous telemetry, tuning alert policies, and addressing configuration drift, advanced capabilities remain shelfware. Software licenses supply the raw mechanism; vigilant human oversight delivers the actual protection.
How do managed security services prevent business email compromise (BEC)?
Managed services prevent business email compromise by enforcing strict identity controls, mailbox auditing, and real-time behavioral monitoring. Engineers block legacy authentication protocols, enforce modern multi-factor validation, and restrict illicit application consents. Concurrently, monitoring systems identify suspicious inbox forwarding rules and impossible-travel logins, allowing security teams to revoke compromised user sessions before financial theft or fraudulent communications occur.
Can managed Microsoft 365 security services assist with industry compliance?
Yes, managed microsoft 365 security services directly support regulatory compliance by maintaining strict technical controls, persistent audit logging, and continuous posture reporting. Specialists align your tenant with rigorous standards like HIPAA, CMMC, and NIST baselines. This verifiable oversight satisfies strict cyber insurance mandates, preserves mandatory evidentiary audit trails, and simplifies external compliance reviews for executive leadership.