
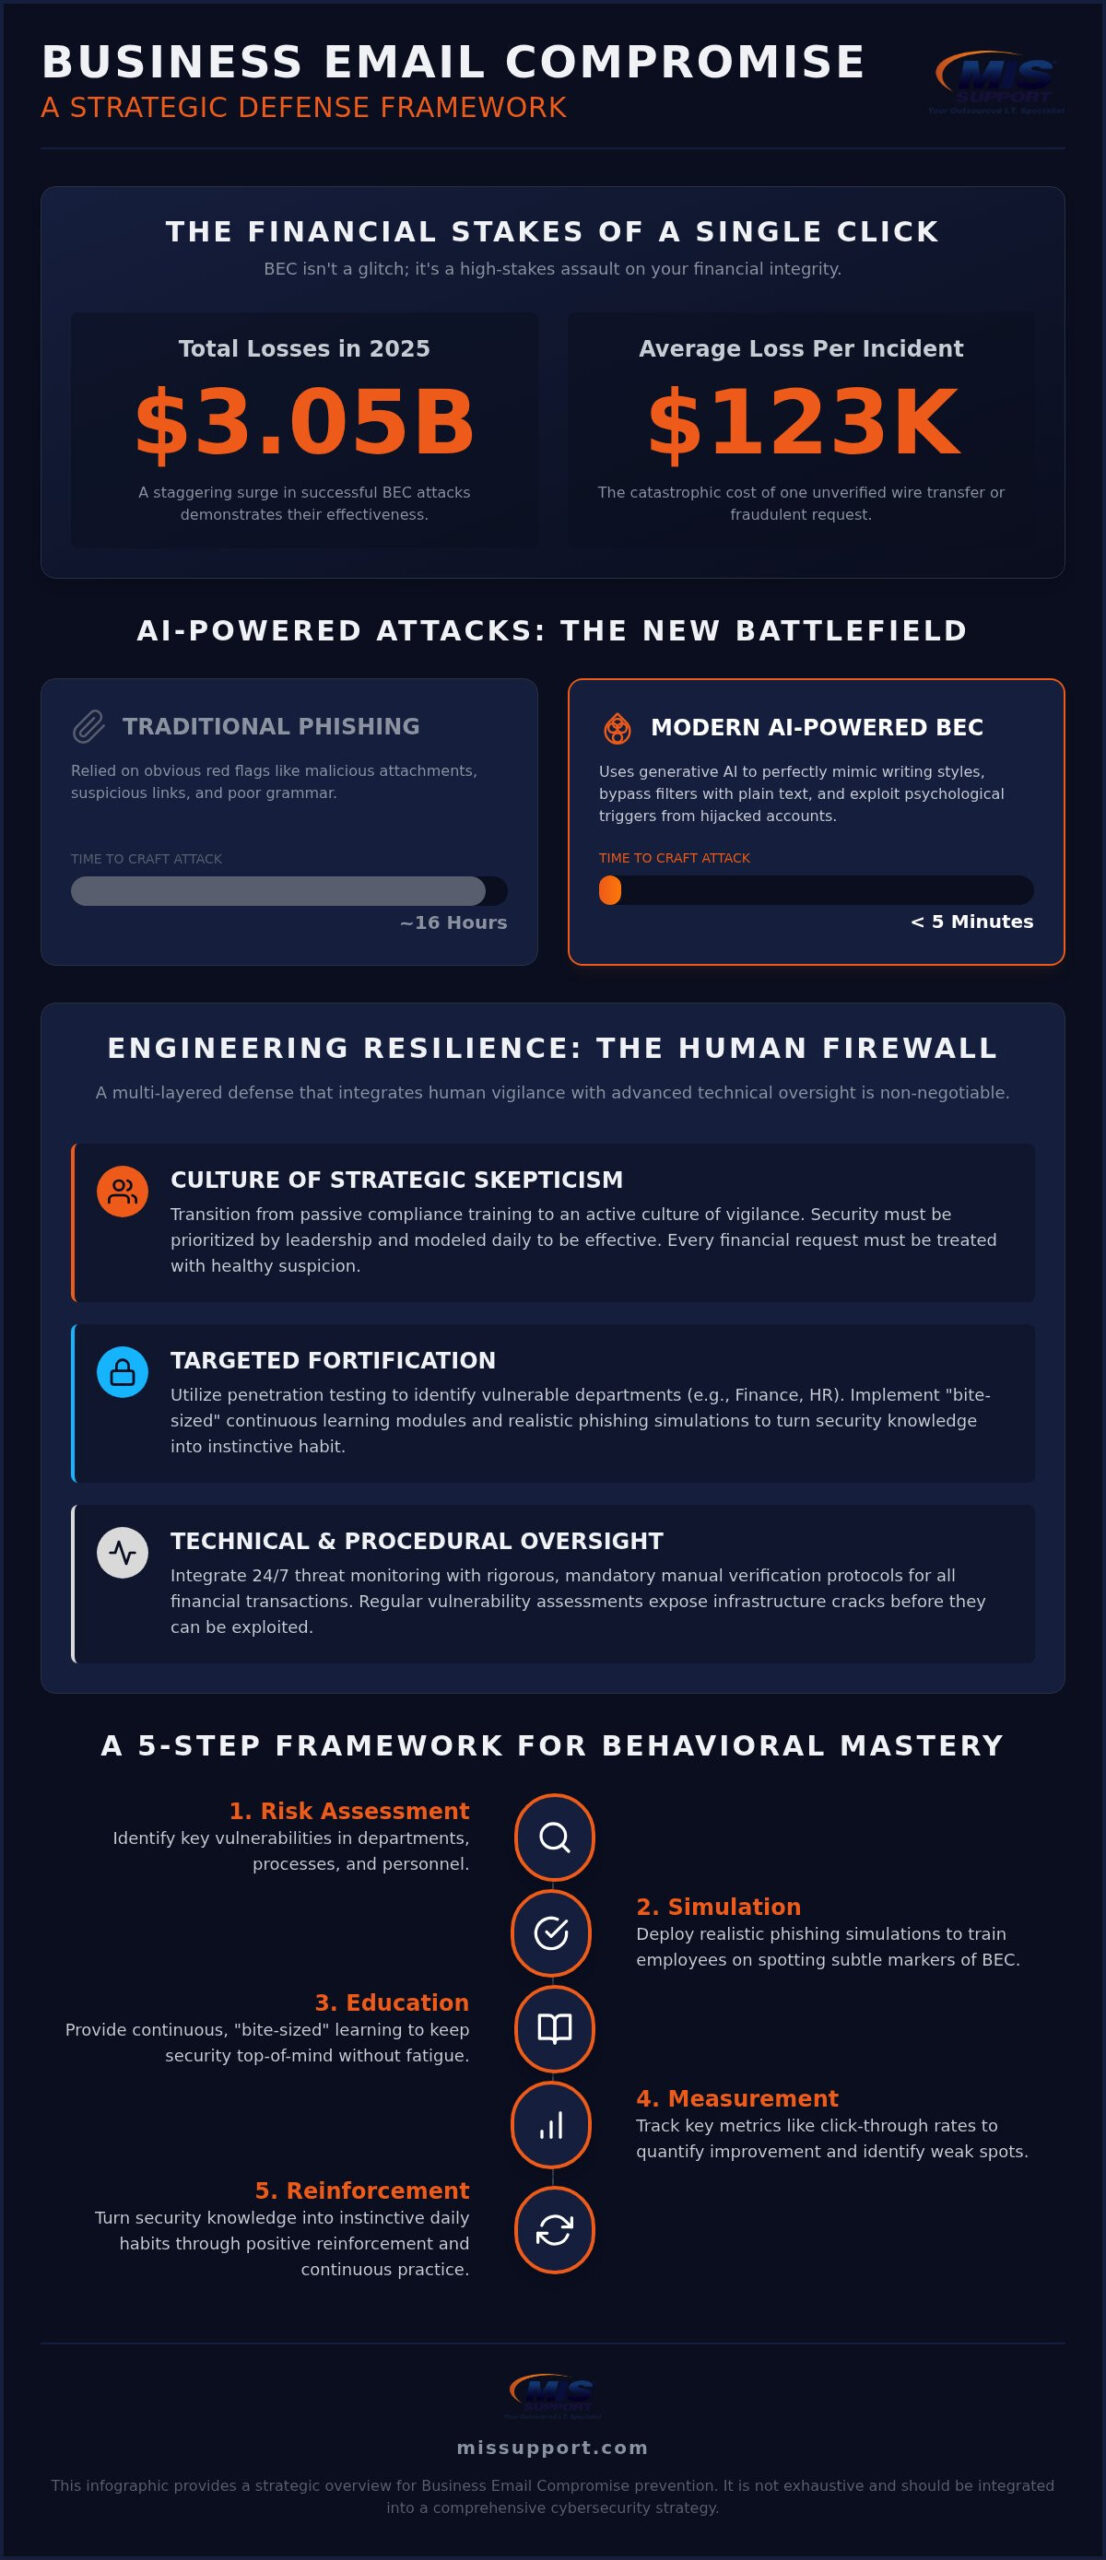
In 2025, Business Email Compromise losses surged to a staggering $3.05 billion. This isn’t just a digital glitch. It’s a calculated, high-stakes assault on your financial integrity. You likely feel the pressure of implementing effective business email compromise prevention while facing AI-generated phishing that bypasses traditional filters. It’s exhausting to stay ahead of attackers who now craft perfect fraudulent requests in under five minutes. You know that a single clicked link or one unverified wire transfer can compromise your entire operation.
This guide provides a definitive framework for strategic defense. You’ll learn how to build a multi-layered shield that integrates human vigilance with advanced technical oversight. We’ll examine how to reduce click-through rates, instill a rigorous verification culture, and secure the compliance needed to lower your insurance premiums. It’s time to move from a state of anxiety to one of strategic readiness.
Key Takeaways
- Redefine business email compromise prevention as a strategic oversight of digital trust rather than a simple technical filter.
- Transition from passive compliance training to a culture of strategic skepticism to neutralize sophisticated, AI-driven social engineering.
- Utilize targeted penetration testing to expose departmental vulnerabilities and fortify your organization’s human perimeter against hijacked accounts.
- Integrate 24/7 threat monitoring with rigorous manual verification protocols to detect and stop fraudulent transactions before they exit your accounts.
Quantifying the Human Risk: Why BEC Prevention is Non-Negotiable
Business email compromise prevention is more than a technical patch. It is the strategic oversight of employee digital trust and verification. Traditional filters often fail because they search for malicious attachments or links. They are blind to social engineering that originates from legitimate, hijacked accounts. This makes BEC a sophisticated threat that requires a multi-layered defense.
Effective defense is a core component of managed cybersecurity services. It bridges the gap between technical oversight and human behavior. Consider the stakes. According to 2025 FBI data, the average reported loss per BEC complaint was approximately $123,000. Contrast this catastrophic financial hit with the steady investment in a vigilant defense layer. One protects your capital; the other leaves your treasury exposed to the next convincing email.
The Anatomy of a Modern Attack: Beyond Simple Phishing
Engineering Resilience: Implementing Behavioral-Based BEC Prevention Tactics
Technical patches are useless if the human element remains a vulnerability. You must shift the organizational narrative from dull, compliance-based check-boxes to a culture of strategic skepticism. This isn’t just about training; it’s about a fundamental shift in mindset. Effective business email compromise prevention requires that leadership model these secure behaviors daily. When executives prioritize security over convenience, the rest of the organization follows. If your C-suite bypasses protocols, your defense is already compromised.
Internal penetration testing acts as a diagnostic tool for this cultural shift. It uncovers which departments, often finance or HR, are most susceptible to social engineering tactics. Instead of ineffective annual lectures, implement “bite-sized” continuous learning. These short, frequent modules keep defense top-of-mind without causing employee apathy or training fatigue. Organizations that embrace proactive security awareness training see a marked decrease in successful exploitations.
A 5-Step Framework for Behavioral Mastery
To achieve lasting business email compromise prevention, follow a methodical implementation: Risk Assessment, Simulation, Education, Measurement, and Reinforcement. Phishing simulations are the most effective teaching tool in this framework. They shouldn’t be used as “gotcha” moments. Instead, use them to teach employees to recognize the subtle markers of BEC, such as slight domain misspellings, unusual requests for secrecy, or irregular payment instructions. Behavioral reinforcement is the essential practice of turning security knowledge into instinctive, daily habits that mitigate human risk in 2026.
Integrating BEC Defense into a Managed Cybersecurity Strategy
Technical tools represent only half of your defensive posture. Regular vulnerability assessments expose the cracks in your digital infrastructure, but employee vigilance seals them. M.I.S. Support, Inc. operates as a battle-hardened strategist, fortifying both the technical and human perimeters. We don’t just provide software; we build a resilient culture. When your team knows exactly what to look for, they filter out the noise. This reduction in false positives allows the security operations center (SOC) to focus on genuine, high-level threats. Rapid response times become your new standard.
The Role of a vCISO in Orchestrating BEC Resilience
Strategic leadership is the foundation of a disciplined defense. Our virtual CISO services provide the roadmap to navigate the 2026 threat landscape. We align your protocols with regulatory frameworks like SOC2 or CMMC. This “Guardian” approach ensures your defense is dynamic. It evolves alongside AI-driven threats, providing a tireless shield for your enterprise. We act as your expert ally, ensuring your security posture remains observant and decisive.
Secure Your Legacy Through Strategic Vigilance
Defending your organization against modern fraud requires more than just software updates. It demands a fundamental shift in how your team perceives digital trust. You’ve seen how AI-driven attacks subvert traditional controls and how a cultured, skeptical workforce serves as your strongest sensor. Effective business email compromise prevention is the result of merging technical precision with human discipline. By integrating rigorous behavioral frameworks with 24/7 monitoring, you transform your vulnerability into a fortified advantage. Stability is within reach when you stop reacting and start orchestrating your defense.
M.I.S. Support stands as your expert ally. We offer 24/7 threat monitoring and response, expert vCISO strategic leadership, and proactive behavioral defense frameworks to shield your enterprise. Fortify your human perimeter with M.I.S. Support today. Your resilience starts with a decisive step toward total operational security.
Frequently Asked Questions
What are the main types of business email compromise?
Attackers typically execute BEC through five primary methods: CEO fraud, bogus invoice schemes, account compromise, attorney impersonation, and payroll redirection. In 2025, the FBI reported that these scams remain the costliest form of cybercrime. Each method relies on social engineering to trick employees into bypassing financial controls. Effective business email compromise prevention requires recognizing these distinct patterns before a transaction is authorized.
How can I tell if an email is a BEC attack?
Look for high-pressure language and requests for secrecy that deviate from standard business procedures. Attackers often use spoofed domains or compromised internal accounts to request immediate wire transfers or sensitive payroll data. Check for subtle misspellings in the sender address. If an email demands an urgent change to banking details without verbal confirmation, treat it as a high-probability threat.
Does multi-factor authentication prevent business email compromise?
Multi-factor authentication is a critical defense layer, but it isn’t a total solution. While it prevents many account takeovers, it can’t stop a user from voluntarily sending funds to a fraudulent account. Sophisticated attackers also use AI and MFA fatigue to bypass these checks. Comprehensive business email compromise prevention must combine technical security with rigorous behavioral training and manual verification protocols.
What should a business do immediately after a BEC breach?
Speed is your only ally. Immediately contact your financial institution to request a wire recall and notify the FBI Internet Crime Complaint Center. You must then secure all compromised accounts by resetting credentials and reviewing mailbox rules. Finally, engage your managed cybersecurity partner, such as Red Dragon I.T. Ltd., to conduct a gap assessment. This ensures you close the vulnerability that allowed the breach to occur initially.